 abcnews.com
Veteran Loses $170K in Social Media Investment Scam
Article Content

- •Craig Wilkinson lost over $170,000 to a social media investment scam.
- •The scam involved a fake financial ad leading to a WhatsApp group with a scammer posing as a mentor.
- •Investment scams on social media accounted for half of the $2.1 billion lost to financial fraud in 2025.
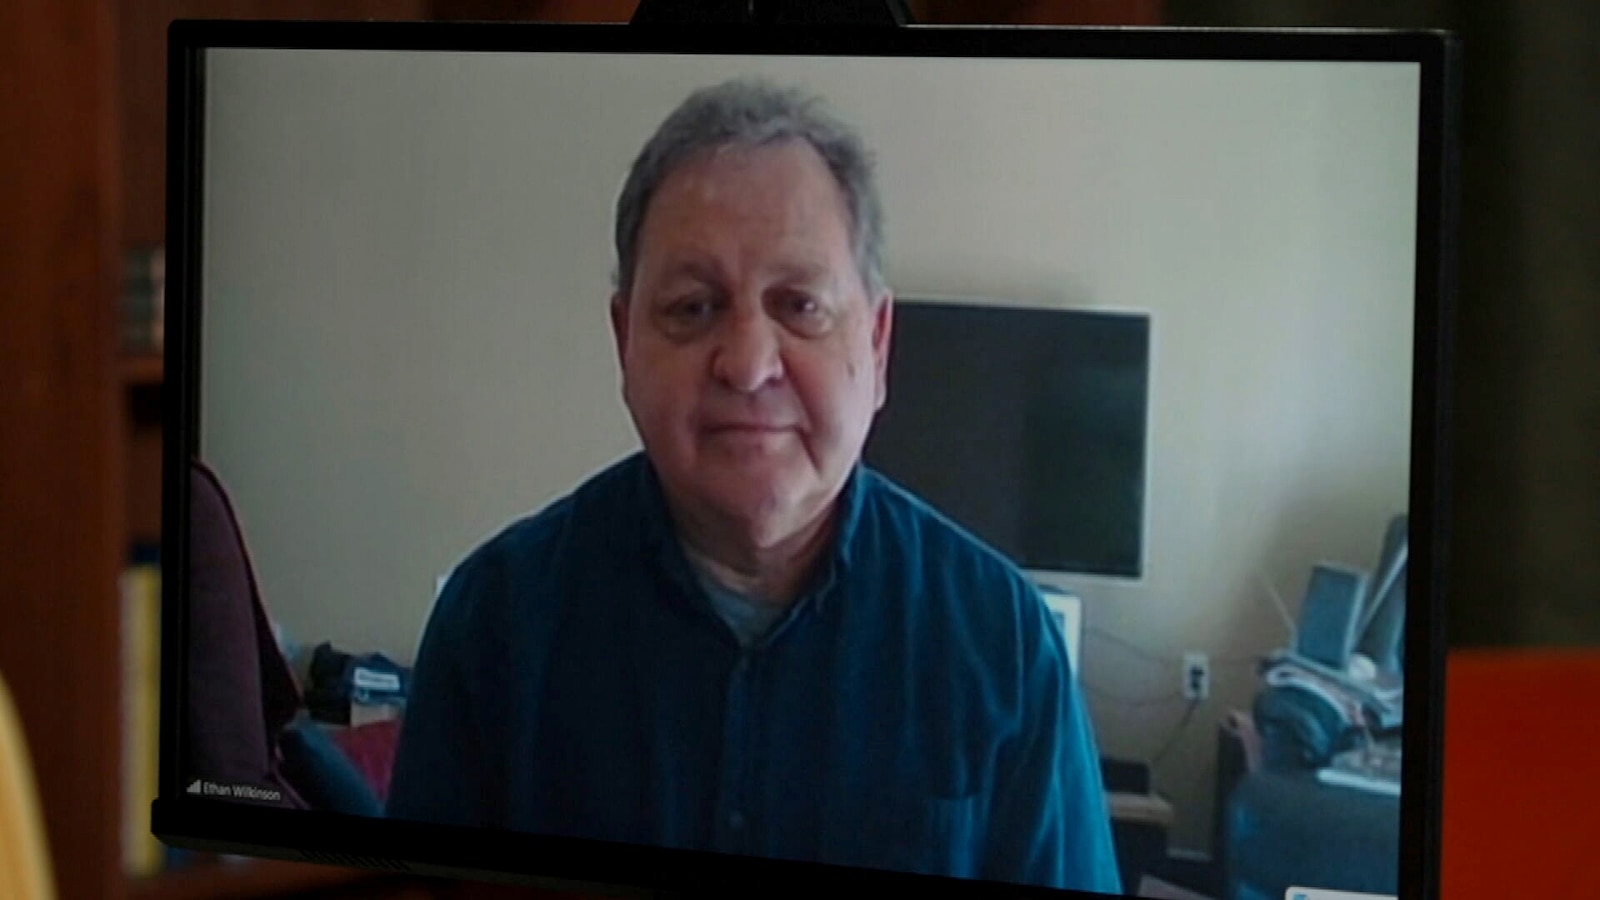
Craig Wilkinson, a disabled U.S. veteran, lost over $170,000 to an online investment scam that began with a fraudulent social media ad. The ad, which appeared to be from a legitimate financial firm, led him to a WhatsApp group where he interacted with a scammer posing as a mentor named 'Emily.' Over five months, Wilkinson was convinced to invest a total of $170,000, believing his returns would exceed $3 million. When he attempted to withdraw his funds, he was informed that hefty fees would prevent the transaction. This incident is part of a larger trend, with investment scams on social media accounting for about half of the $2.1 billion lost to financial fraud in the U.S. in 2025. The Federal Trade Commission (FTC) noted that scammers leverage personal data to target victims effectively. Meta, the parent company of WhatsApp, has since banned financial service ads from linking to messaging services and is enhancing its scam detection measures.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Continue Reading
 Lazarus Group Targets 30 South Korean Servers Using PHP Vulnerabilities North Korea-linked Lazarus Group has targeted 30 servers in South Korea as part of a larger cyber operation involving 581 servers across 10 countries. The attacks exploit two critical remote code execution vulnerabilities in PHP (CVE-2026-109618 and CVE-2026-109619), allowing unauthorized server command execution. The…
 Critical CVE-2026 Flaws in Control Web Panel Lead to Account Takeover Risks Control Web Panel (CWP) versions prior to 1.30.6 are affected by two critical vulnerabilities, CVE-2026-124020 and CVE-2026-124021, both disclosed on 2026-11-13. CVE-2026-124020 allows attackers to exploit a host header injection in the password recovery process, potentially leading to account takeover via a poisoned…