 abnormal.ai
ZeroTokens Phishing Platform Enables Real-Time Attacks on Financial Institutions
Article Content

- •ZeroTokens allows real-time monitoring and manipulation of phishing attacks.
- •Over 45,000 phishing emails targeted 24,000 recipients across 700 organizations.
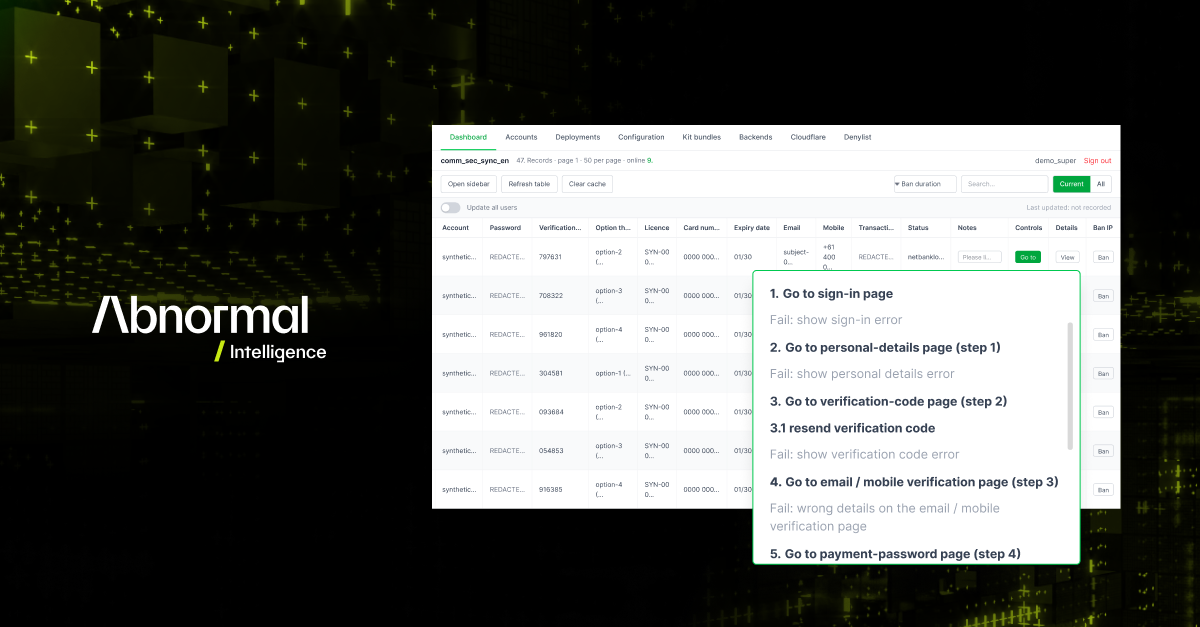
- •The platform mimics legitimate financial institution verification processes.
The ZeroTokens phishing platform has been identified as a sophisticated tool enabling real-time phishing attacks against financial institutions. Attackers can monitor victims' sessions and adapt prompts based on the information entered, allowing for the collection of sensitive data such as login credentials and personal identification. Over 45,000 phishing emails were sent to more than 24,000 recipients, targeting over 700 organizations. The campaign utilized ten sender domains and nine compromised SendGrid accounts, successfully passing SPF, DKIM, and DMARC checks. The phishing scheme leveraged W-8BEN tax-documentation reviews to create a believable pretext for the victims. ZeroTokens mimics the verification processes of 53 financial institutions and can present multiple stages of interaction. The platform does not facilitate direct financial transactions but allows attackers to use collected data for subsequent fraud. Abnormal AI published its findings on August 25, 2026, detailing the operational mechanics of ZeroTokens and its implications for cybersecurity defenses.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 Critical BeyondTrust 9.3 Vulnerability Actively Exploited by Threat Actor A critical vulnerability (CVE-2026-102764) in BeyondTrust Remote Support has been discovered and is actively being exploited by the threat group ARMORY CASTLE, reportedly linked to China. The vulnerability, which has a CVSS score of 9.3, allows unauthenticated attackers to upload files and potentially compromise host…
 Critical SQL Injection Zero-Day in Arista VeloCloud Orchestrator Exploited Arista Networks has patched a critical zero-day vulnerability (CVE-2026-114625) in its VeloCloud Orchestrator (VCO) that is actively being exploited. The flaw allows authenticated users, even those with basic privileges, to escalate their access to superuser status via a low-complexity SQL injection attack. This…