 Unherd
Coordinated Arson Attacks Target Jewish Sites in London
Article Content

- •Four Jewish sites in London have been attacked in one week, indicating a coordinated campaign.
- •The group Harakat Ashab al-Yamin al-Islamiya is behind the attacks, using Telegram for coordination.
- •Increased police presence and calls for government action highlight the urgent need for community safety.
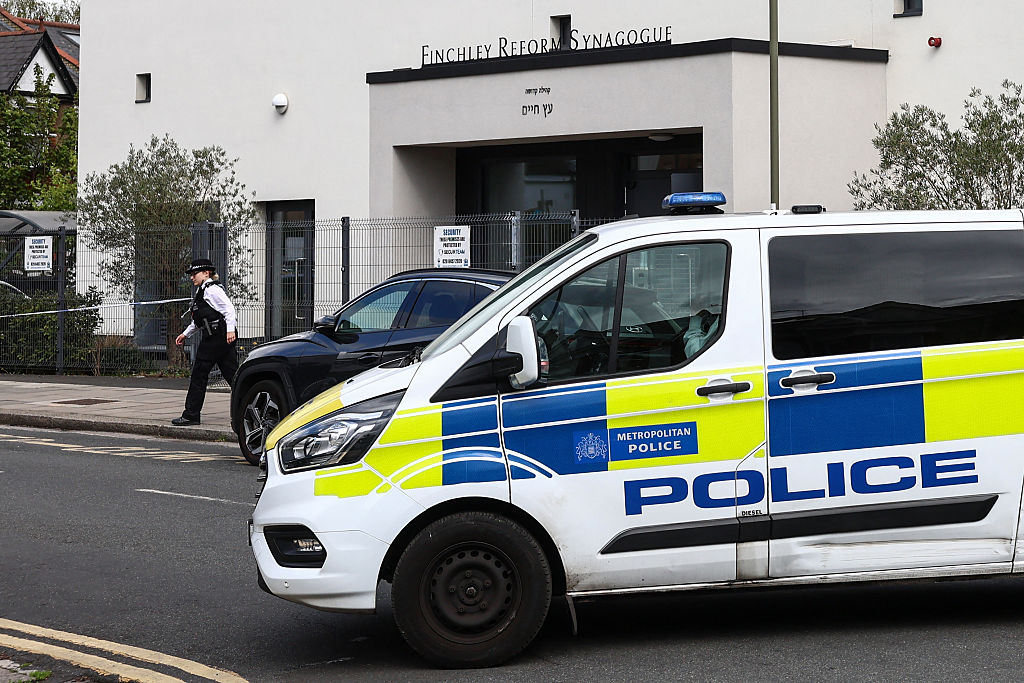
A series of arson attacks targeting Jewish sites in London has escalated, with four incidents reported in one week. The latest attack occurred at Kenton United Synagogue on April 19, 2026, where an incendiary device was thrown through a window, causing minor damage. Previous attacks included petrol bombings at Finchley Reform Synagogue and an attempted arson at a Jewish charity in Hendon. Chief Rabbi Ephraim Mirvis described these incidents as a 'sustained campaign of violence and intimidation' against the Jewish community. The group behind the attacks, Harakat Ashab al-Yamin al-Islamiya (Hayi), has claimed responsibility, using Telegram to coordinate and publicize their actions. Police have increased security measures in Jewish neighborhoods, but the government is urged to proscribe Hayi under terrorism laws. No injuries have been reported, but the fear and tension within the community are palpable. The situation reflects a broader trend of antisemitic violence in the UK.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (25)
Following this threat?
Track Finchley Reform Synagogue in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 Silent Lynx Targets CIS Governments via WinRAR Exploit The threat actor Silent Lynx has launched a series of attacks against government organizations in the Commonwealth of Independent States (CIS) from June 2025 to August 2026. These attacks exploit a vulnerability in WinRAR (CVE-2025-8088) to deploy reverse shells, including FoalShell and PickleShell, facilitating…