 Thecyberexpress
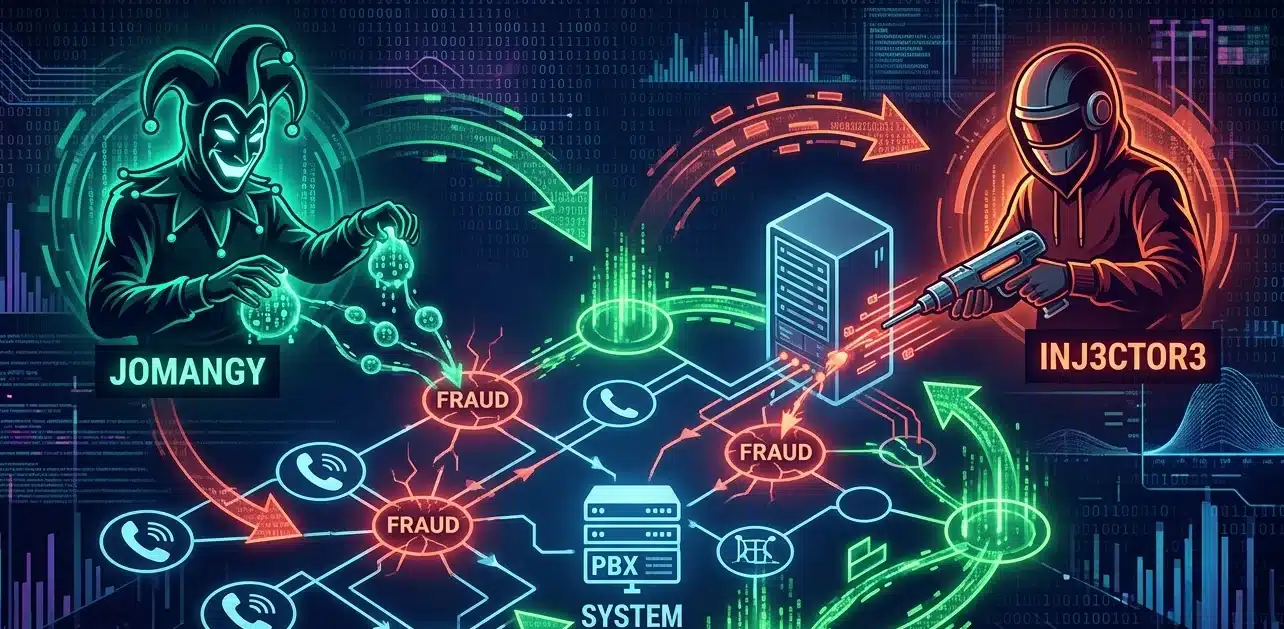
INJ3CTOR3 Targets FreePBX Systems with JOMANGY Webshell and VoIP Toll Fraud
Article Content

- •INJ3CTOR3 is exploiting FreePBX systems using a new webshell called JOMANGY.
- •The campaign employs a six-layer persistence mechanism, making removal difficult.
- •Eighteen backdoor accounts, including nine with root access, enhance the attack's stealth.
A cyber campaign attributed to the threat actor INJ3CTOR3 is targeting FreePBX systems, deploying a new PHP webshell named JOMANGY. This operation utilizes a six-layer persistence mechanism to maintain control over compromised systems, allowing attackers to exploit victims' SIP trunks for fraudulent VoIP calls. The campaign has introduced 18 backdoor accounts, nine of which have root-level access, making detection challenging. Researchers from Cyble Research & Intelligence Labs (CRIL) have linked this activity to previous operations involving the ZenharR malware toolkit. The attack leverages vulnerabilities such as CVE-2025-64328 and CVE-2025-57819 to gain initial access. The scope of impact is global, with a significant focus on systems hosted on Alibaba Cloud. Current remediation efforts are largely ineffective due to the self-healing nature of the malware.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (5)
Following this threat?
Track Inj3ctor3, Jomangy and Alibaba Cloud in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical Cisco FMC Vulnerabilities Under Active Exploitation Cisco's Secure Firewall Management Center (FMC) Software has two critical vulnerabilities, CVE-2026-20079 and CVE-2026-20316, that are currently being exploited by state-sponsored and ransomware actors. CVE-2026-20079, rated 10.0 on the CVSS scale, allows unauthenticated remote attackers to bypass authentication and…
 Critical GitLab CVE-2026-85706 Exploited; Microsoft Issues Record 974 Patches A critical CVE-2026-85706 path-traversal vulnerability in GitLab (CVSS 10.0) was exploited in the wild just hours after its disclosure on September 12, 2026. Microsoft released its largest-ever patch batch, addressing 974 vulnerabilities, including several actively exploited Windows flaws. The GitLab flaw allows…