Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
A cyber campaign attributed to the threat actor INJ3CTOR3 is targeting FreePBX systems, deploying a new PHP webshell named JOMANGY. This operation utilizes a six-layer persistence mechanism to maintain control over compromised systems, allowing attackers to exploit victims' SIP trunks for fraudulent...
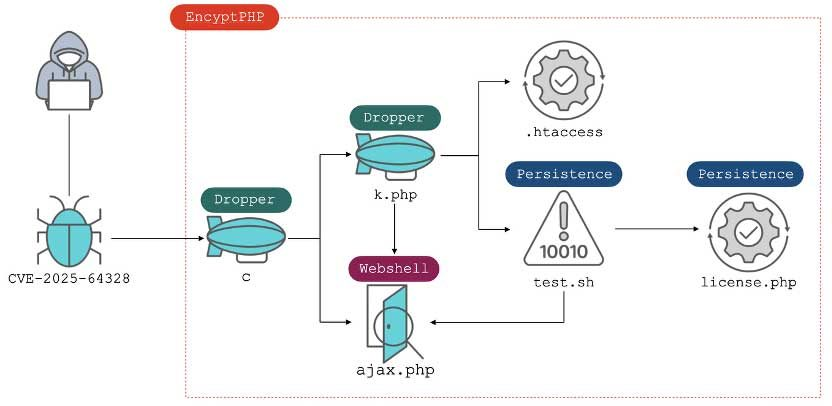
Approximately 900 Sangoma FreePBX systems are compromised due to CVE-2025-64328, a command injection vulnerability. This bug was patched in version 17.0.3, but many systems remain unpatched and vulnerable to exploitation. The vulnerability was added to the CISA KEV list on February 3, 2026, indicati...
Attackers exploited CVE-2025-64328, a command injection vulnerability, affecting 900 Sangoma FreePBX systems. The exploitation resulted in the installation of web shells, with hundreds of instances remaining compromised since attacks began in December 2025.
Hackers are exploiting a critical vulnerability in FreePBX, specifically CVE-2025-64328, to deploy a persistent webshell named EncystPHP. This attack, attributed to the group INJ3CTOR3, allows complete administrative control over compromised VoIP systems. The campaign began in early December 2025, t...