 Bleepingcomputer
Shai-Hulud Malware Compromises 25K GitHub Repositories via npm Packages
Article Content
Browse articles 
The Shai-Hulud malware has re-emerged, infecting over 500 trojanized npm packages and compromising secrets from more than 25,000 developers within three days. The malicious packages, including those from popular services like Zapier and Postman, were added to the npm registry and automatically posted encoded data to GitHub. This supply-chain attack is a continuation of a campaign that first surfaced in September 2025.
Ask AI about this cluster
Answers cite the sources they use
Updated 219d ago How this analysis works
More articles in this cluster (4)
Following this threat?
Track Shai-hulud and AsyncAPI in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
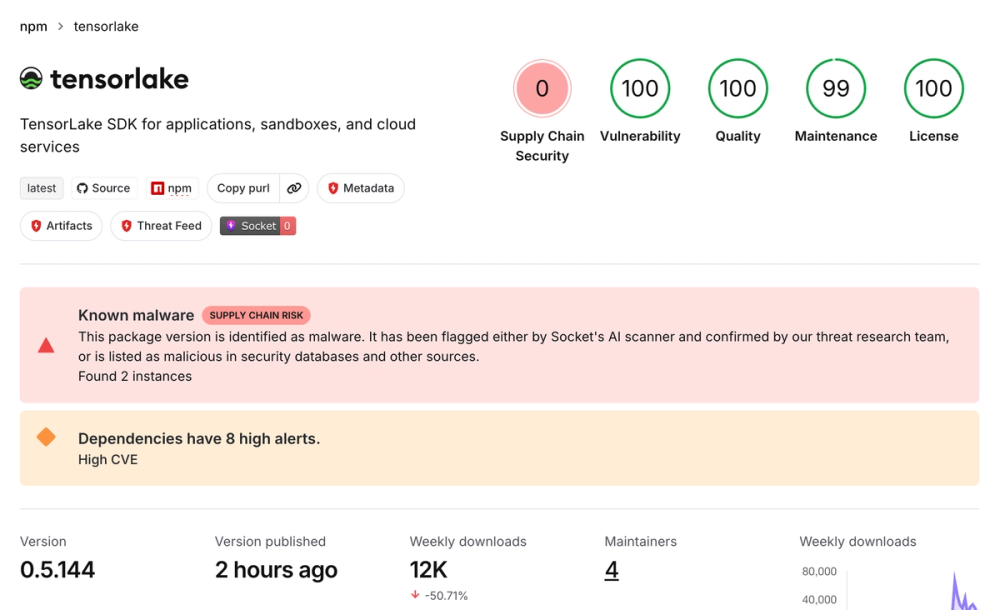 Tensorlake npm Package Compromised by Shai-Hulud Worm On October 8, 2026, the Tensorlake npm package version 0.5.144 was compromised, delivering a credential-stealing worm known as Shai-Hulud. The malware, which was published through a compromised maintainer account, executes a preinstall hook that runs an obfuscated loader to harvest credentials from local files and CI…
 Cisco Email Bug Exploited as Zero-Day by Unknown Actors A zero-day vulnerability in Cisco's email system has been by unknown criminals. The flaw, described as a 'make-me-root' bug, allows attackers to gain root access via email. Cisco has not disclosed specific details about the vulnerability or the affected systems. The exploit is reportedly being used in the wild…